2026. június 11.
Enterprise Firewall Core Adds a Dedicated High-Throughput Security Gateway
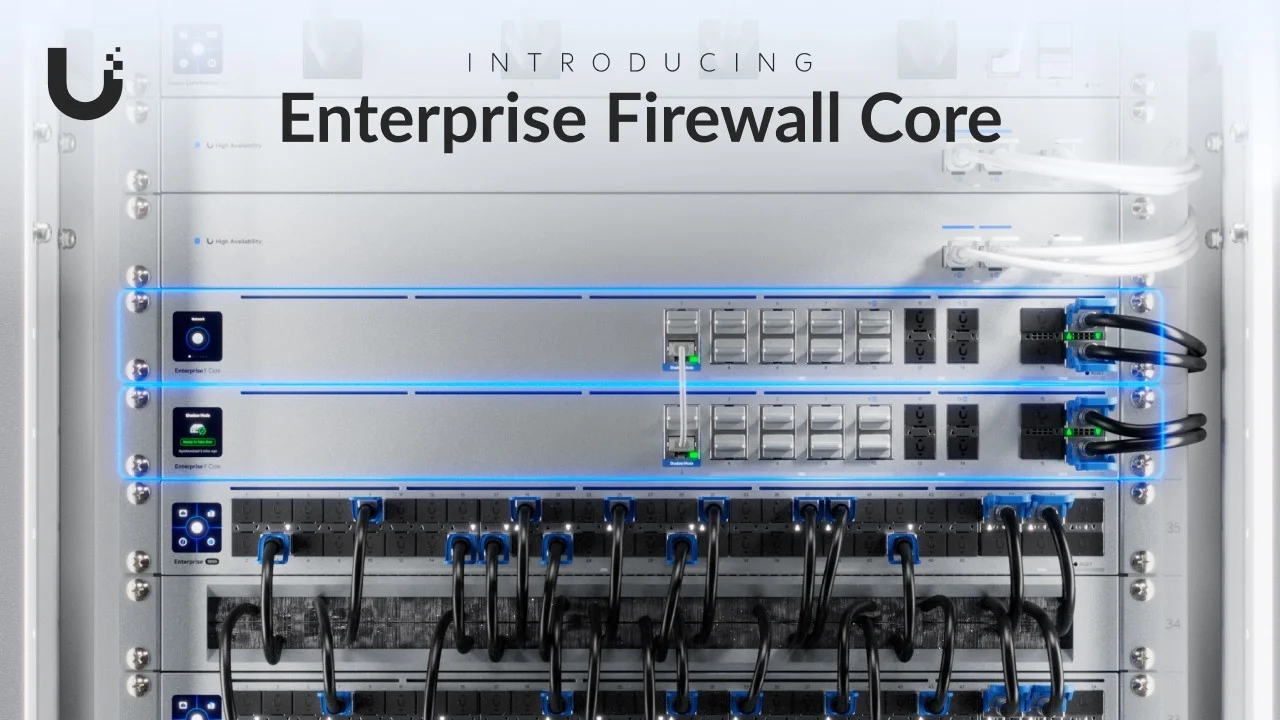
The Enterprise Firewall Core takes the hyperscale compute architecture Ubiquiti proved out in the Dream Machine Beast and scales it up for genuinely large deployments. It's built for the point where a consumer-grade gateway has become the actual bottleneck on the network.
Compute built for scale
At its core sit 24 Neoverse N2 cores, supporting up to 22,000 active devices and 10 million concurrent sessions. For larger office campuses and municipal networks running dozens of cameras, access points, and staff devices on one network, that headroom matters. Security inspection stops being the thing that slows everything else down as the device count grows.
Threat detection that keeps up with encrypted traffic
Threat detection runs at up to 79 Gbps, checked continuously against tens of thousands of signatures through Proofpoint's real-time threat intelligence. Full SSL inspection runs at up to 61 Gbps, so encrypted traffic, which is most traffic on any modern network, doesn't become a blind spot.
For healthcare organizations and municipalities with real compliance obligations around network security, that combination gives genuine visibility into encrypted traffic without turning it into the performance bottleneck.
Connecting a lot of sites at once
The Enterprise Firewall Core also works as a serious SD-WAN anchor: more than 5,000 concurrent IPsec or WireGuard tunnels, and up to 38 Gbps of aggregate IPsec throughput. A municipality or property group connecting several sites, multiple municipal buildings or a portfolio of offices, gets secure site-to-site connectivity that scales with the portfolio instead of straining under it.
Built to stay up
High availability comes through VRRP-enabled Shadow Mode, with Multi-Chassis Link Aggregation and switch stacking extending resiliency further into the network. Hot-swappable fans and redundant power supplies round out the hardware side. That reliability matters most at sites where downtime is not just inconvenient but a real operational or safety issue.
One policy, every site
Unified management runs through Site Manager, with identity-aware policy enforcement via Entra, Google Workspace, or LDAP. For offices already using one of those identity providers, network access policy follows the same staff directory as everything else, applied the same way at every site instead of configured separately per location.